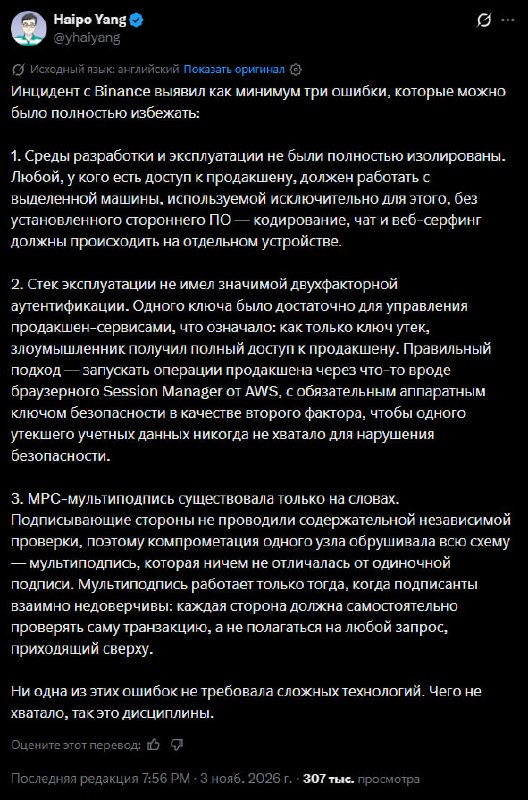
CoinEx Founder Names Three Mistakes in Binance Security Hypo Yang believes the $6.34 billion Binance hack was made possible by avoidable security errors. lack of insulation. Access to critical infrastructure should only be done from individual protected devices, without third-party software. Weak access protection. Compromise on credentials alone should not give full control over the system. Hardware multi-factor authentication is required. Problems with MPC multi-signatures. Signers must verify each transaction independently rather than automatically approving requests.
According to Young, the problem was not a lack of technology, but a lack of compliance with basic safety rules.