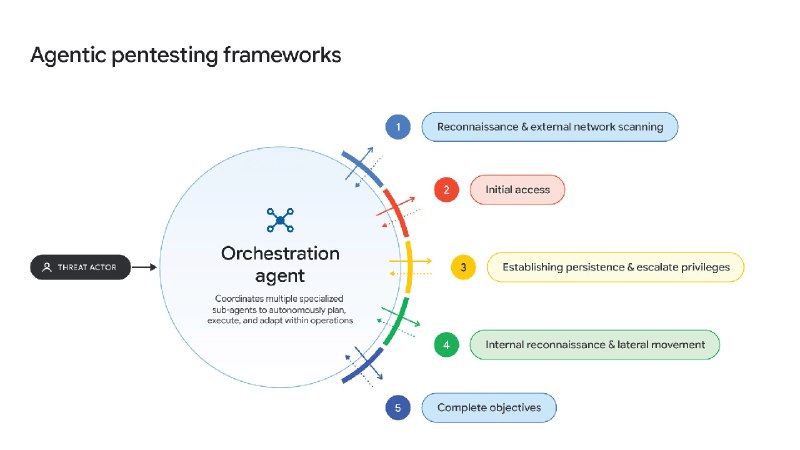
AI agents transition from hacking to assisted autonomous penetration workflows.
The Google GTIG assessment claims that threat actors are using multi-agent frameworks like CAIRN and PentaGI to automate patch distribution, day-of-day exploits, credential theft, and cloud LLM abuse. The observed activity included scans across Asia, a focus on the US aerospace sector, and LLM hijacking incidents that yielded up to $1 million in fraudulent use prior to containment.
The key change is not a new profession but compressed timelines. GTIG findings indicate that operators are sacrificing stealth for speed, chaining known techniques for faster exploitation and monetization cycles. For defenders, behavioral traces and action patterns are now more important than static signatures.
Open sources - closed narratives.