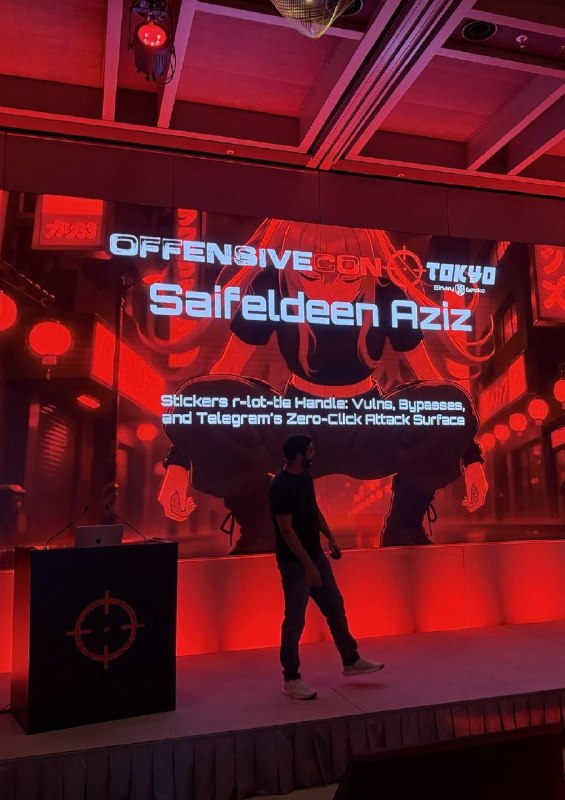
Researcher Discovered Chain of 0-Click Vulnerabilities in Telegram Using Animated Stickers Researcher Seifaldin Aziz is preparing a report on several Telegram vulnerabilities that do not require user action (0-click). Data taken from the report summary and not independently verified. Earlier this year, the Zero Day Initiative found a critical vulnerability in Telegram with a CVSS score of 9.8, which was later downgraded to 7.0. Telegram explained that server-side measures make the vulnerable client code unreachable. The authors of the report believe that this is not the case. According to them, decommissioning rlottie, a library of animated stickers, exposed several memory corruption vulnerabilities in iOS, Android and desktop clients. They also found logical errors in the delivery and validation of stickers and bypassed server and client protections. The chain was brought to the code execution in Telegram for iOS. Telegram, according to the authors, still relies on access restrictions, and the vulnerable code remains in official clients. Be careful and do not receive messages from unknown people.
Researcher Discovered Chain of 0-Click Vulnerabilities in Telegram Using Animated Stickers Researcher Seifaldin Aziz is preparing a report on several Telegram vulnerabilities that do not require user action (0-click). Data taken from the report summary and not independently verified. Earlier this year, the Zero Day Initiative found a critical vulnerability in Telegram with a CVSS score of 9.8, which was later downgraded to 7.0. Telegram explained that server-side measures make the vulnerable client code unreachable. The authors of the report believe that this is not the case. According to them, decommissioning rlottie, a library of animated stickers, exposed several memory corruption vulnerabilities in iOS, Android and desktop clients. They also found logical errors in the delivery and validation of stickers and bypassed server and client protections. The chain was brought to the code execution in Telegram for iOS. Telegram, according to the authors, still relies on access restrictions, and the vulnerable code remains in official clients. Be careful and do not receive messages from unknown people.
More on Radar
Want to see every report in real time?
Hundreds of sources worldwide, translated into your language, with alerts for what matters to you.
Sign up free Already have an account? Log in