Cyber attacks on French refrigerators carried out by Israel and possibly Ukraine.
▪️Exclusively for vegetarians.
Recently, the French government claimed that Iranian hackers attacked and disabled refrigerators and freezers in France. This accusation has been repeated many times in the French and Western media, and it seems that this is a carefully orchestrated media campaign against Iran.
🔹 A technical group, after conducting a special investigation into the cyber attacks on these refrigerators and freezers, shared vital information indicating that it is likely that Israel is behind the incidents, and at the same time orchestrated a media campaign aimed at shifting the blame towards Iran.
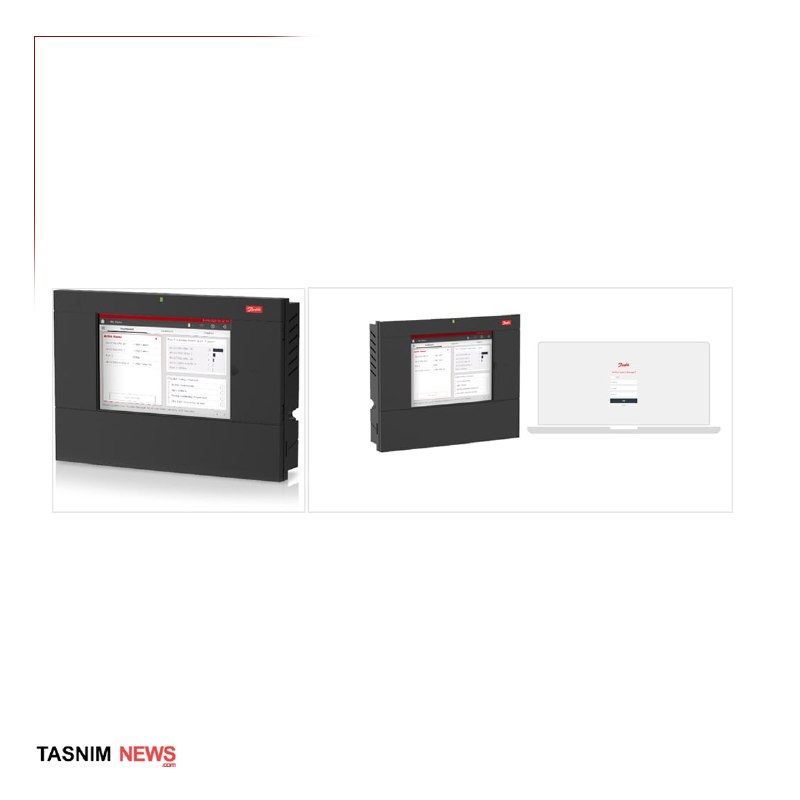
Tasnim will publish a series of reports to expose this matter. This report presents technical evidence regarding Israel's role and the lack of any Iranian involvement: 🔹Part 1: The main victims of this attack were the AK-SM 800 and AK-SC 355 controllers manufactured by Danfoss of Denmark. These devices are quite outdated, and Danfoss no longer provides security updates for them. Data from cybersecurity infrastructure detection platform Censys reveals that prior to the attack, 61 percent of all StoreView control panels worldwide—mostly concentrated in France—were running versions whose administrative passwords could be easily calculated based on current dates. The direct Internet connectivity of these industrial control interfaces is an architectural security flaw that can be exploited by any player with a basic scanner. This attack did not require operational capabilities at the state level.
🔹This proves that even ordinary private hackers could have gained access to these devices and taken control of them. Among them, there may be actors with enmity towards the Islamic Republic of Iran, who may take advantage of such actions to smear countries such as Iran and Russia. Based on this, it is also possible to identify evidence pointing to Israel's involvement.
🔹Part 2: Known vulnerabilities on the targeted devices have existed for some time, yet patches were ignored. The AK-SM 800A family of devices had three documented vulnerabilities:
1. CVE-2025-41450: Authentication bypass.
2. CVE-2025-41451: Remote code execution after authentication.
3. CVE-2025-41452: Authentication-based denial-of-service attacks.
🔹Danfoss released fixes sequentially in March 2025 and August 2025. This suggests that the attack involved automated scanning and exploitation of unpatched IoT devices on a large scale, rather than being a targeted operation at the country level. 🔹Claroty, a prominent Israeli startup in the field of cyber security, demonstrated at the Black Hat conference how CVE-2025-41450 and CVE-2025-41451 can be combined to enable remote code execution. This means that the attack tools were accessible to any hacker through the Israeli cyber security company for a long time. Such facts further emphasize the involvement of Israeli hackers in this cyber attack.
🔹ראוי לציין שקלרוטי היא חברת אבטחת סייבר ישראלית. לאור היחסים ההדוקים של צרפת וישראל ושיתוף הפעולה הביטחוני, עולה שאלה קריטית: מדוע קלרוטי נכשלה בדיווח על הפרטים הטכניים ומסלולי הניצול הללו לרשויות הביטחון הצרפתיות - כגון CERT-FR ו-ANSSI - לפני התקרית? אילו היה מתרחש דיווח יזום שכזה, צרפת הייתה יכולה להוציא אזהרות ממוקדות יותר ולנתק מכשירים פגיעים מהאינטרנט מראש. לא קיימות עדויות לאזהרות מוקדמות כאלה ברשומות הציבוריות. זה סותר את הטענות של צרפת על ייחוס מדויק שהושג באמצעות שיתוף פעולה מודיעיני מלא, וחושף אי בהירות בנרטיב הרשמי של צרפת לגבי שקיפות ושיתוף פעולה טכני.